
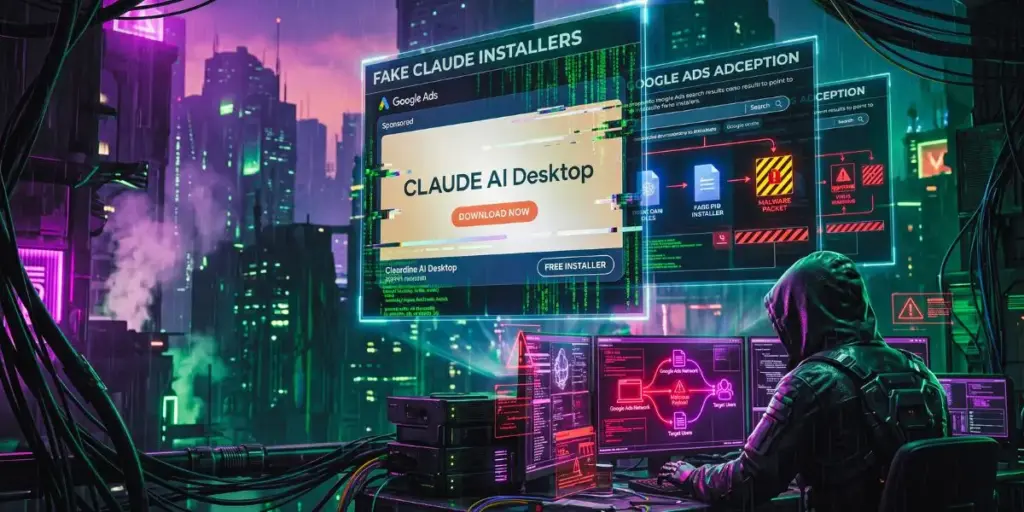

A Google search for “Claude Mac” should lead you to Anthropic’s official download page. Instead, security researchers found sponsored results that appeared to point to Bing, redirected through a compromised retailer website, and delivered a fake Claude installer designed to trick macOS users into running malicious Terminal commands.
The campaign, named Adception by researchers at Push Security, abuses Google Ads, legitimate Bing click-tracking redirects, and multiple layers of cloaking to reach victims. Its final page imitates Claude’s official macOS installation instructions, but its “Copy” button places a malicious command on the clipboard instead of Anthropic’s legitimate installer command.
This article explains who is targeted, how the attack works, why it is difficult for security scanners to detect, and the exact precautions Mac users and businesses should take.
What Happened in the Fake Claude Campaign?
Cybercriminals used sponsored Google search results to send people searching for “claude mac” to fake Claude installation pages. The attack was discovered by Push Security and reported by BleepingComputer on October 9, 2026.
Unlike ordinary malvertising, the Google ad did not visibly lead to an unknown attacker domain. It displayed the legitimate bing.com domain as its destination. After the user clicked, the ad passed through Google’s advertising redirect, then Bing’s bing.com/ck/a click-tracking endpoint, then a compromised WordPress site belonging to a South American retailer, and finally reached claude-desk-code[.]com, a fraudulent Claude download page.
The attackers did not need to compromise Google or Bing itself. They abused trusted infrastructure and normal redirect mechanisms to make a malicious journey look legitimate at every step.
The Attack Chain at a Glance
Why Is This Called ‘Adception’?
Adception is the name Push Security gave to a malvertising technique that hides a malicious redirect chain inside legitimate advertising and search-engine infrastructure. The term reflects the layered nature of the attack: an ad inside a trusted search experience, a redirect inside a trusted Bing tracking link, and another redirect inside a compromised website.
The technique is designed to defeat two groups:
-
Users, who may trust the visible Bing domain and assume the sponsored result is safe.
-
Automated security scanners, which may not reproduce the exact referrer, browser headers, and JavaScript behavior required to reach the final payload.
That combination makes Adception more sophisticated than a basic fake-download ad. It is not simply “a bad ad”; it is a deliberately staged funnel that abuses trust signals at several points.
In plain terms, the attacker rents the top of the search results page. A user looking for Claude desktop, Claude AI download, or Claude installer sees a sponsored link. The landing page mimics official branding. The downloaded file may be named ClaudeSetup.exe, Claude_Installer.dmg, or ClaudeDesktop.msi. When executed, it acts as a dropper or loader. It may display a fake installation animation while quietly fetching a second-stage payload.
How Does the Fake Claude Installer Trick Work?
The fake Claude page displays Anthropic’s legitimate macOS installation command, but the copy action substitutes a malicious command. This is a ClickFix-style attack: the victim is persuaded to copy and run a command themselves, turning them into the person who executes the payload.
On the fraudulent page, the visible command is:
curl -fsSL https://claude.ai/install.sh | bashThat command appears legitimate because it points to Anthropic’s official Claude domain. However, clicking the page’s copy button places a different command in the clipboard. The substituted command prints a message claiming to download Claude from Anthropic, then decodes a Base64-encoded URL pointing to lake-90[.]com. It uses curl to download a .dat file from attacker-controlled infrastructure and pipes it directly into macOS’s Z shell, zsh, for execution.
The victim may see claude.ai in the fake page and in the Terminal output, yet the code actually being run comes from somewhere else entirely.
Fake Claude installers work so well because sponsored search results borrow the credibility of Google Ads while AI hype pushes users to download desktop apps quickly. Claude has become a shorthand for capable assistant software. People want offline access, larger context handling, file workflows, or simply a desktop shortcut. That demand creates a narrow window: search, click, install, start working. Attackers compress that window into a single malicious ad.
Brand impersonation is not new. Criminals have long faked browser updates, PDF readers, VPN clients, and team collaboration tools. AI tools add two accelerants:
-
The market changes fast. Users may not know whether an official desktop app exists, which version is current, or where Anthropic distributes it.
-
AI tools promise productivity. The perceived payoff feels high enough to override caution.
The attack also exploits platform trust transfer. A user may distrust a random .exe from a forum, but a Google Ads result can feel vetted. That assumption is wrong. Advertising platforms moderate campaigns, yet attackers use cloaking, disposable domains, compromised websites, and rapid rotation to slip past review. By the time a bad ad is removed, dozens or hundreds of victims may have clicked.
The Psychology Behind the Click
Three human habits make the scheme effective:
-
Position bias: The first result feels authoritative.
-
Label blindness: Many users skim the small “Ad” tag.
-
Installation muscle memory: Software installs are routine, so a progress bar feels normal.
Add urgency language—“Download now,” “Limited access,” “Official desktop beta”—and the brain stops treating the file as risk. It treats it as errands.
Why the Clipboard Is the Attack Surface
The clipboard creates a gap between what a user sees and what a user executes.
-
The page shows a safe-looking command.
-
The user clicks “Copy.”
-
The clipboard receives a different command.
-
The user pastes it into Terminal without inspecting it.
-
The command downloads and executes attacker-controlled code.
This is why “just read the command before running it” is good advice, but not sufficient on its own. A sophisticated fake page can make visual verification difficult, especially when the user expects a normal software installation process.
Expert insight: Treat any instruction that says “copy this into Terminal” as a high-risk action, even if the website looks polished. Legitimate software vendors may provide Terminal commands, but you should verify the source and inspect the command before execution.
Who Is Most at Risk?
The primary targets are macOS users searching for Claude, particularly people who use Google to find the app and click sponsored results without checking the final domain.
The campaign is especially relevant for:
-
Developers searching for Claude, Claude Code, or AI development tools.
-
Freelancers and agency workers who install AI apps on work machines.
-
Small-business users who may not have endpoint detection or security training.
-
IT teams that allow employees to install software without an approved software catalog.
-
Anyone who routinely copies Terminal commands from web pages.
The final payload had not been publicly identified at the time of reporting, so it would be premature to claim exactly what malware, if any, was delivered. What is confirmed is that the fake page attempted to make victims download and execute attacker-controlled code.
Why Google Ads Malvertising Is Effective
Google Ads malvertising works because sponsored results occupy prominent positions and inherit some of the trust associated with the search engine. Users often distinguish less carefully between organic results and advertisements, especially when they are searching for a specific product name.
In this campaign, the attackers added another trust layer by using Bing’s legitimate click-tracking URL as the visible ad destination. BleepingComputer reported that the sponsored result displayed bing.com, which made the advertisement appear less suspicious than a direct link to an unfamiliar domain.bleepingcomputer
The attackers also used cloaking. The compromised WordPress site checked for a Bing referrer and specific browser headers before redirecting visitors. The fake Claude site used JavaScript to confirm that the visitor had arrived from Google or Bing. Anyone who accessed the malicious URL directly was sent to a 404 page.
What Makes This Campaign Harder to Detect
Is Claude or Anthropic Compromised?
There is no evidence in the reported campaign that Anthropic’s Claude platform, Claude.ai, or its official installer was compromised. The malicious infrastructure was separate: attackers used Google Ads, Bing redirects, a compromised WordPress site, and a fake Claude download page.
The real Claude installation command was displayed on the fake page, which likely increased credibility. But the malicious action occurred when the page’s copy button replaced that command with a different, obfuscated command.
This distinction matters. The lesson is not “avoid Claude.” The lesson is: download Claude only from Anthropic-controlled domains and never execute a Terminal command copied from an unverified advertisement or third-party installation page.
How to Avoid Fake Claude Installers on Mac
The safest approach is to bypass search ads entirely and go directly to Anthropic’s official website. For Claude, use claude.ai or anthropic.com, then navigate to the official download or installation section from there.
Safe Download Checklist
-
Type
claude.aioranthropic.comdirectly into the browser. -
Avoid clicking sponsored results for software downloads.
-
Check the browser address bar before entering credentials or downloading files.
-
Confirm the domain exactly; look for unusual spellings, hyphens, or extra words.
-
Do not trust a page merely because it uses Anthropic branding, screenshots, or a familiar installation command.
-
Never paste a Terminal command without reading every character.
-
Compare copied commands against the command displayed on the official source.
-
Prefer official app stores or vendor-controlled download pages when available.
-
Keep macOS, browsers, and security tools updated.
-
Report suspicious ads through Google’s ad reporting tools.
Pro tip: If you must use a Terminal command, paste it into a plain-text editor first. Look for curl, wget, bash, zsh, base64, eval, pipes, or unexpected domains. If anything differs from the command shown on the official vendor page, stop.
What Should Businesses Do?
Businesses should treat AI-tool searches as a software-supply-chain risk. Employees searching for Claude, ChatGPT, Gemini, Cursor, or development utilities can encounter fake installers, credential-harvesting pages, and ClickFix lures.
A practical defense combines user awareness, endpoint controls, and network monitoring.
Business Protection Steps
-
Publish an approved software list. Tell employees exactly where to obtain approved AI tools.
-
Block or warn on risky domains. Use DNS filtering, secure web gateway policies, and endpoint protection to flag newly registered or suspicious domains.
-
Restrict unnecessary Terminal use. Developers may need Terminal access, but general staff usually do not.
-
Monitor for suspicious execution. Alert on
curlorwgetpiped intobashorzsh, especially when followed by Base64 decoding or unknown domains. -
Require device management. Use MDM to control installations, enforce updates, and collect telemetry from managed Macs.
-
Train employees on ClickFix attacks. Teach staff that “copy and run this command” is a common social-engineering pattern.
-
Create an incident-reporting path. Make it easy for employees to report a suspicious ad, download, or Terminal command immediately.
-
Assume compromise after execution. If someone ran an unknown command, isolate the device, preserve logs, rotate credentials, and investigate before restoring normal use.
A Practical Response Plan if You Ran the Command
If you copied a command from a suspicious Claude page and ran it in Terminal, act quickly. Do not wait to see whether something obvious breaks.
-
Disconnect the Mac from the internet. This limits further command-and-control communication or data exfiltration.
-
Do not enter passwords or approve prompts. Avoid giving a potentially malicious process more access.
-
Preserve evidence. Keep the Terminal window, browser history, downloaded files, and screenshots if possible.
-
Run a security scan. Use updated endpoint protection and macOS built-in security tools.
-
Inspect login items and persistence. Review LaunchAgents, LaunchDaemons, login items, browser extensions, and scheduled jobs.
-
Rotate credentials from another trusted device. Prioritize email, cloud storage, password managers, code repositories, cloud consoles, and financial accounts.
-
Revoke active sessions and API tokens. Attackers may attempt to reuse authenticated sessions or stolen tokens.
-
Seek professional incident response if the Mac contains business data, customer records, source code, or privileged cloud access.
Because the final payload in the reported campaign was unknown, assume risk rather than waiting for confirmation of a specific malware family.bleepingcomputer
How the Attack Chain Unfolds: From Ad Click to Malware Execution
The attack chain unfolds when a paid search ad leads a user to a counterfeit download page, a signed-looking installer runs, and a dropper fetches the final payload. The sequence is simple enough to reproduce across campaigns, yet modular enough to evade basic blocklists.
-
Keyword targeting: The adversary bids on terms such as “Claude download,” “Claude AI desktop,” “Claude installer,” “Anthropic Claude app,” and misspellings. Brand bidding lowers cost and increases reach.
-
Malicious ad creation: The ad copy uses official logos, product screenshots, and language lifted from documentation or press releases. It may claim “Windows version available” or “Fast local setup.”
-
Landing page spoofing: The destination page imitates Anthropic’s design. It may use a lookalike domain, a subdirectory on a compromised site, or a temporary cloud storage page. Some pages include fake reviews or countdown timers.
-
Payload delivery: The user downloads an installer. On Windows, it may be an executable, MSI, or script-wrapped package. On macOS, it may be a DMG or PKG. The file icon and metadata can be forged.
-
Execution and distraction: The installer shows a progress bar, license screen, or “connecting to Claude” animation. Meanwhile, it writes files to
AppData,Temp, orPublicfolders. -
Second-stage retrieval: The dropper contacts a command-and-control server. It may download an infostealer, remote access trojan, cryptocurrency miner, or ransomware preload.
-
Persistence: The malware creates scheduled tasks, registry Run keys, startup folder entries, or launch agents. On macOS, it may abuse login items or configuration profiles if the user grants permissions.
-
Impact: Credentials, browser sessions, cookies, wallet files, documents, and API keys are collected. In enterprise environments, the foothold can lead to lateral movement or data exfiltration.
Cloaking Helps the Ad Survive Review
Attackers often serve different content to automated reviewers and real victims. A security crawler may see a benign page. A targeted user, filtered by geography, device, referrer, or timing, receives the malicious download. This makes takedown slower and detection harder.
Pro Tip: If a software download page asks you to disable antivirus, allow notifications, install a browser extension, or run a script to “verify age,” leave immediately. Legitimate AI assistants do not need those steps to install.
What Malware Do Fake Claude Installers Deliver?
Fake Claude installers usually deliver commodity malware such as infostealers, remote access trojans, downloaders, cryptominers, or ransomware loaders rather than a genuine Claude client. The installer itself is rarely the final weapon. It is a delivery truck. The cargo depends on the criminal group’s monetization model.
| Payload Type | Typical Behavior | Why Attackers Use It | User-Visible Signs |
|---|---|---|---|
| Infostealer | Harvests saved passwords, cookies, autofill data, crypto wallets, and session tokens | Fast monetization through credential resale | Browser logouts, unexpected password resets, MFA prompts |
| Remote Access Trojan (RAT) | Gives attacker interactive control over the device | Enables espionage, file theft, and follow-on attacks | Webcam/mic indicators, strange processes, sluggish performance |
| Downloader/Loader | Fetches additional modules after installation | Modular campaigns evade static detection | Repeated network connections to unknown domains |
| Cryptominer | Uses CPU/GPU to mine cryptocurrency | Steady revenue with low interaction | Fan noise, heat, reduced battery life, slow apps |
| Ransomware Preload | Drops encryption components or gathers system info | High payout in enterprise attacks | Shadow copy deletion, unusual file access, backup disruption |
The most common early-stage pattern is a downloader. It may be unsigned or signed with a stolen certificate. It may use legitimate tools—PowerShell, rundll32, mshta, wscript, curl, or macOS shell commands—to blend in. That living-off-the-land approach makes endpoint detection harder, especially if the organization lacks tuned EDR rules.
Why macOS Is Not Immune
Apple’s Gatekeeper and notarization raise the bar, but they do not end the risk. Users can right-click open a blocked app, approve a profile, or ignore warnings after social engineering. A fake Claude DMG may instruct the victim to disable security settings temporarily. Once the app is allowed, persistence mechanisms can follow.
How to Spot a Fake Claude Installer Before You Run It
You can spot a fake Claude installer by checking the domain, file name, publisher metadata, price prompts, and behavior requests before execution. The goal is to slow the click down just enough for verification to matter.
Checklist
-
Verify the publisher domain. Anthropic-related services are typically distributed through official channels such as
anthropic.comandclaude.ai; verify current official pages before downloading. If the page uses an odd domain, a URL shortener, Dropbox, a GitHub release from an unknown account, or a blogspot page, treat it as suspicious. -
Do not trust the ad position. Paid placement is not endorsement. Check organic results, official documentation, and vendor announcements.
-
Inspect the file properties. On Windows, right-click the installer, choose Properties, and review Digital Signatures. A valid signature from Anthropic or a known parent company is a positive signal. Missing, invalid, or unrelated signatures are red flags.
-
Watch for impossible promises. “Unlimited free Claude Pro,” “offline GPT/Claude hybrid,” or “jailbroken Claude desktop” are marketing bait, not legitimate distribution.
-
Be suspicious of extra steps. Legitimate installers should not require you to disable Defender, allow unknown sources, run a Command Prompt script, or install a random browser extension.
-
Check hash reputation cautiously. If an official checksum is published, compare it. Do not upload the file to public hash reputation services if it may contain sensitive data or if policy forbids it.
-
Use a sandbox or VM first. For security teams, detonate the installer in an isolated environment and monitor process creation, network connections, registry changes, and persistence.
Quick Red-Flag Table
| Signal | Likely Official | Likely Fake |
|---|---|---|
| Domain | anthropic.com / claude.ai or verified app store listing |
Lookalike domain, free hosting, shortened URL |
| Payment | Clear pricing through official account flow | Upfront crypto payment, “unlock full model” fee |
| Installer behavior | Standard install, minimal permissions | Disables AV, runs scripts, requests admin unnecessarily |
| Communication | Support through official channels | Telegram/Discord “activation key” instructions |
| Version info | Consistent release notes | Vague “latest build” with no changelog |
Expert Insight: The fastest way to train users is not a long policy document. It is a one-page visual: official domain, signature check, and three phrases that mean stop. Make the stop rule memorable.
How Organizations Should Respond to Adception-Style Malvertising
Organizations should respond to Adception-style malvertising by combining network controls, endpoint allowlisting, browser isolation, rapid isolation procedures, and role-based user training. A single awareness email will not stop a determined user who believes they need Claude for a deadline. Defense needs friction in the right places.
Technical Controls That Reduce Risk
-
DNS and web filtering: Block newly registered domains, suspicious URL shorteners, and categories associated with malware or anonymous hosting. Do not rely solely on reputation feeds; attackers rotate infrastructure quickly.
-
Browser isolation or remote browsing: For high-risk roles, render web downloads in an isolated environment. This reduces the chance that a malicious installer reaches the endpoint intact.
-
Application allowlisting: Permit only approved software installers. If users cannot execute arbitrary files from Downloads or AppData, droppers lose much of their power.
-
EDR telemetry tuning: Alert on installer processes spawning PowerShell,
certutil,bitsadmin,curl,wscript,mshta, or unusual outbound connections. Track parent-child relationships, not just file hashes. -
Controlled folder access: Protect browser credential stores, SSH keys, API token folders, and document repositories from unauthorized writes.
-
MFA and conditional access: Even if cookies or passwords are stolen, strong phishing-resistant MFA reduces account takeover impact.
-
Patch and baseline management: Keep browsers, OS, and remote tools updated. Remove local admin rights where feasible.
Process Controls That Matter
-
Software request workflow: Give employees a safe route to request approved AI tools. If the official path is slow, users will find unsafe paths.
-
Vendor verification page: Maintain an internal list of approved AI domains and download procedures.
-
Incident playbook: Define who isolates the host, who resets credentials, who preserves memory, and who communicates with legal or customers.
-
Tabletop exercise: Run a scenario where a user clicks a fake Claude ad. Measure detection time, containment time, and credential reset coverage.
Pro Tip: Do not wait for a perfect policy. Start with three controls: block execution from user-writable temp folders, require approval for installers, and force browser sign-out plus credential reset after any suspected installer execution.
Case Study: How a Developer Could Encounter It
Imagine a freelance developer needs Claude on a new MacBook. They search Google for “claude mac.” A sponsored result appears near the top. The destination shows bing.com, so the developer clicks it.
The page loads quickly and looks convincing. It uses Claude branding, offers a macOS installer, and shows the familiar curl command from Anthropic. The developer clicks Copy, opens Terminal, pastes the command, and presses Enter.
Nothing obviously happens at first. The command prints a reassuring message about downloading Claude. But behind the scenes, the command has decoded a hidden URL, downloaded a .dat file, and passed it to zsh for execution.
The developer’s mistake was not technical ignorance. It was reasonable trust placed in a familiar interface, a legitimate-looking command, and a sponsored search result. That is exactly why this campaign is effective.
A mid-sized professional services firm experienced an Adception-style incident when a consultant searched for Claude, clicked a sponsored result, and executed a fake Windows installer. The consultant needed a tool to summarize client meeting notes. The ad promised a “Claude desktop beta for Windows.” The landing page looked close enough to the official style. The file was named ClaudeSetup.exe.
Within minutes, the installer displayed a progress bar. Ten minutes later, the consultant noticed browser sessions logging out. The endpoint detection platform flagged rundll32 making an outbound connection to a low-reputation IP. The SOC isolated the laptop before the malware could reach the file server.
The response followed a simple sequence:
-
Isolate the endpoint. The laptop was removed from the network while preserving volatile memory.
-
Reset credentials from a clean device. The consultant’s password, MFA recovery options, email sessions, VPN certificate, and cloud tokens were invalidated.
-
Review SaaS logs. Analysts checked for impossible travel, new API keys, and mailbox rules.
-
Reimage, do not just clean. Because the installer had admin interaction, the device was rebuilt from a trusted image.
-
Update controls. The firm blocked direct execution from Downloads for non-admin users and added a temporary rule alerting on any process named
ClaudeSetupoutside approved directories. -
Communicate without shaming. The consultant became part of the training story. That mattered more than another policy memo.
The incident did not require exotic forensics. It required speed. The malware had not yet completed lateral movement because the EDR alert arrived early and the analyst understood the parent-child process tree. That is the practical lesson: malvertising defense is often a race between user curiosity and organizational containment.
What the Case Reveals
-
The initial access vector was not a vulnerability. It was a purchase decision inside an ad auction.
-
The user was not reckless. The environment made recklessness look reasonable.
-
Detection depended on behavior, not hash reputation.
-
Recovery depended on credential hygiene as much as endpoint cleanup.
How to Recognize ClickFix Attacks
ClickFix attacks persuade users to fix a fake problem or complete an installation by copying and running commands. They often appear on fake software pages, fake CAPTCHA screens, fake error messages, or compromised websites.
Common warning signs include:
-
A page instructing you to press
Command + Space, open Terminal, and paste a command. -
A “Copy” button paired with a Terminal instruction.
-
Commands containing
curl,wget,base64,eval,bash, orzsh. -
A domain that resembles, but does not exactly match, an official vendor domain.
-
Urgent language, fake errors, or claims that a browser or system needs repair.
-
Installation instructions that arrive through an advertisement rather than the vendor’s official site.
The fake Claude campaign fits this pattern precisely: it presented a credible-looking installation flow, then used the clipboard to swap the legitimate command for a malicious one.
What to Do If You Already Installed a Fake Claude App
If you already installed a fake Claude app, disconnect the device, preserve evidence, reset credentials from a clean machine, and run full endpoint remediation before reconnecting. Do not assume that uninstalling the program removes the infection. Many droppers leave persistence behind.
Immediate Steps
-
Take the device offline. Disable Wi-Fi and Ethernet. Do not shut down if memory capture is needed by your security team; for home users, power off only if isolation is not possible.
-
Do not enter more passwords. Assume saved credentials, cookies, and session tokens may be exposed.
-
Use a known-clean device to reset accounts. Change email, banking, cloud storage, password manager master password, and any AI account passwords. Enable or refresh MFA.
-
Revoke active sessions. Sign out everywhere for email, Microsoft 365, Google, Slack, GitHub, VPN, and password manager.
-
Check for unfamiliar extensions and scheduled tasks. On Windows, review Task Scheduler and Startup apps. On macOS, check Login Items, Launch Agents, and configuration profiles.
-
Run a reputable anti-malware scan. For business devices, let IT perform managed remediation. Personal devices may need a clean operating system reinstall for full confidence.
-
Monitor for abuse. Watch credit reports, account recovery emails, unexpected MFA prompts, and unknown API keys.
-
Report the ad. Use the advertising platform’s reporting tool and notify the brand’s security contact. This helps takedown efforts, though it will not undo compromise.
Home User Shortcut
If you are not comfortable with forensic steps, the safest path is: disconnect, reset passwords from another device, back up only essential documents to external media, reinstall the operating system, and restore files after scanning them. Backup images made after infection are not trustworthy.
Key Takeaways
Fake Claude installers spread through Google Ads because attackers rent trust, not because Claude itself is compromised. The Adception pattern is a reminder that paid search can be a malware delivery channel, especially around trending AI brands. The defense is not paranoia. It is verification.
Before downloading any AI tool, confirm the domain, check digital signatures, and refuse installer behavior that asks you to weaken security. For teams, build a safe request path for approved tools, restrict execution from user-writable folders, tune EDR for dropper behavior, and rehearse isolation steps. If a device has already run a suspect installer, treat credentials as exposed and rebuild with confidence rather than hoping cleanup is enough.
Start today with three actions:
-
Bookmark the official Claude and Anthropic pages.
-
Enable phishing-resistant MFA on accounts that support it.
-
Test your incident response plan against a fake installer scenario.
Attackers buy attention. Defenders should make that attention expensive.
FAQs
Are fake Claude installers real?
Yes. Security researchers at Push Security identified a malvertising campaign that used Google Ads and Bing redirects to send macOS users to fake Claude installation pages. The final page attempted to trick users into executing malicious Terminal commands.
What is the Adception attack?
Adception is a malvertising technique that abuses Google Ads and legitimate Bing click-tracking redirects to route users through compromised websites to malicious pages. It uses cloaking to make the final payload harder for scanners and direct visitors to reach.
Is Claude itself infected or compromised?
No evidence indicates that Claude.ai or Anthropic’s official installer was compromised. The attackers impersonated Claude’s installation process and abused third-party advertising and redirect infrastructure to distribute a malicious command.
How do I safely install Claude on Mac?
Go directly to claude.ai or anthropic.com, avoid sponsored search results, and use only installation instructions from Anthropic’s official domain. Before running any Terminal command, inspect it carefully and compare it with the official source.
What should I do if I ran a suspicious Terminal command?
Disconnect from the internet, preserve evidence, run updated security scans, inspect persistence mechanisms, and rotate passwords, sessions, and API tokens from a trusted device. If the Mac has business access, involve IT or incident-response support immediately.
Is the Adception attack a Claude vulnerability?
No. Adception abuses advertising and brand trust to distribute fake installers. Claude itself is not hacked in this scheme. The danger comes from users downloading counterfeit software that appears related to Claude or Anthropic.
Are Google Ads safe for downloading software?
Google Ads can be safer than random links, but they are not proof of legitimacy. Attackers use cloaking and disposable domains. Always verify the publisher domain, digital signature, and official download path before installing any software from a search ad.
How can I tell if a Claude installer is fake?
Check the domain, file name, and digital signature. Suspicious signs include lookalike URLs, missing signatures, requests to disable antivirus, crypto payments, and promises of unlimited free premium access. When in doubt, use the official Anthropic or Claude website.
Can antivirus stop fake Claude installers?
Antivirus helps, but it may miss new or obfuscated droppers. Behavior-based EDR, application allowlisting, DNS filtering, and user verification reduce risk further. No single control is enough; layered defenses catch campaigns that rely on speed and deception.
What should a company do after a fake installer incident?
Isolate the endpoint, preserve logs and memory, reset credentials from a clean device, revoke sessions, reimage the machine, and review SaaS activity. Update controls to block execution from Downloads, improve EDR alerts, and train users on verifying software sources.
Next Steps
Fake Claude installers show how attackers now combine paid search, trusted redirect infrastructure, compromised websites, and social engineering into one convincing attack path. The visible domain, the branding, and even the displayed command can all be legitimate while the action you take becomes dangerous.
Use Anthropic’s official domains, avoid sponsored download links, inspect every Terminal command, and train your team to recognize ClickFix-style instructions. If you manage devices for a business, add AI-tool download guidance to your security policy now—before an employee searches for the next popular AI app and clicks the wrong sponsored result.